History and Fundamentals of Modern Cryptography
May 1, 2026
I. Historical Origins and Evolution
The word cryptography comes from the Greek kryptos (hidden) and graphein (to write). Cryptography addresses the need to protect or authenticate information. Its history spans early concealment and substitution techniques through today's mathematically defined, computer-based systems.
Ancient Civilizations Nonstandard hieroglyphs appear in Egyptian inscriptions from around 1900 BCE, but they are not evidence of a modern cipher or necessarily of secret messages. Substitution ciphers are documented in later historical records; the Caesar cipher is associated with Julius Caesar in the first century BCE.
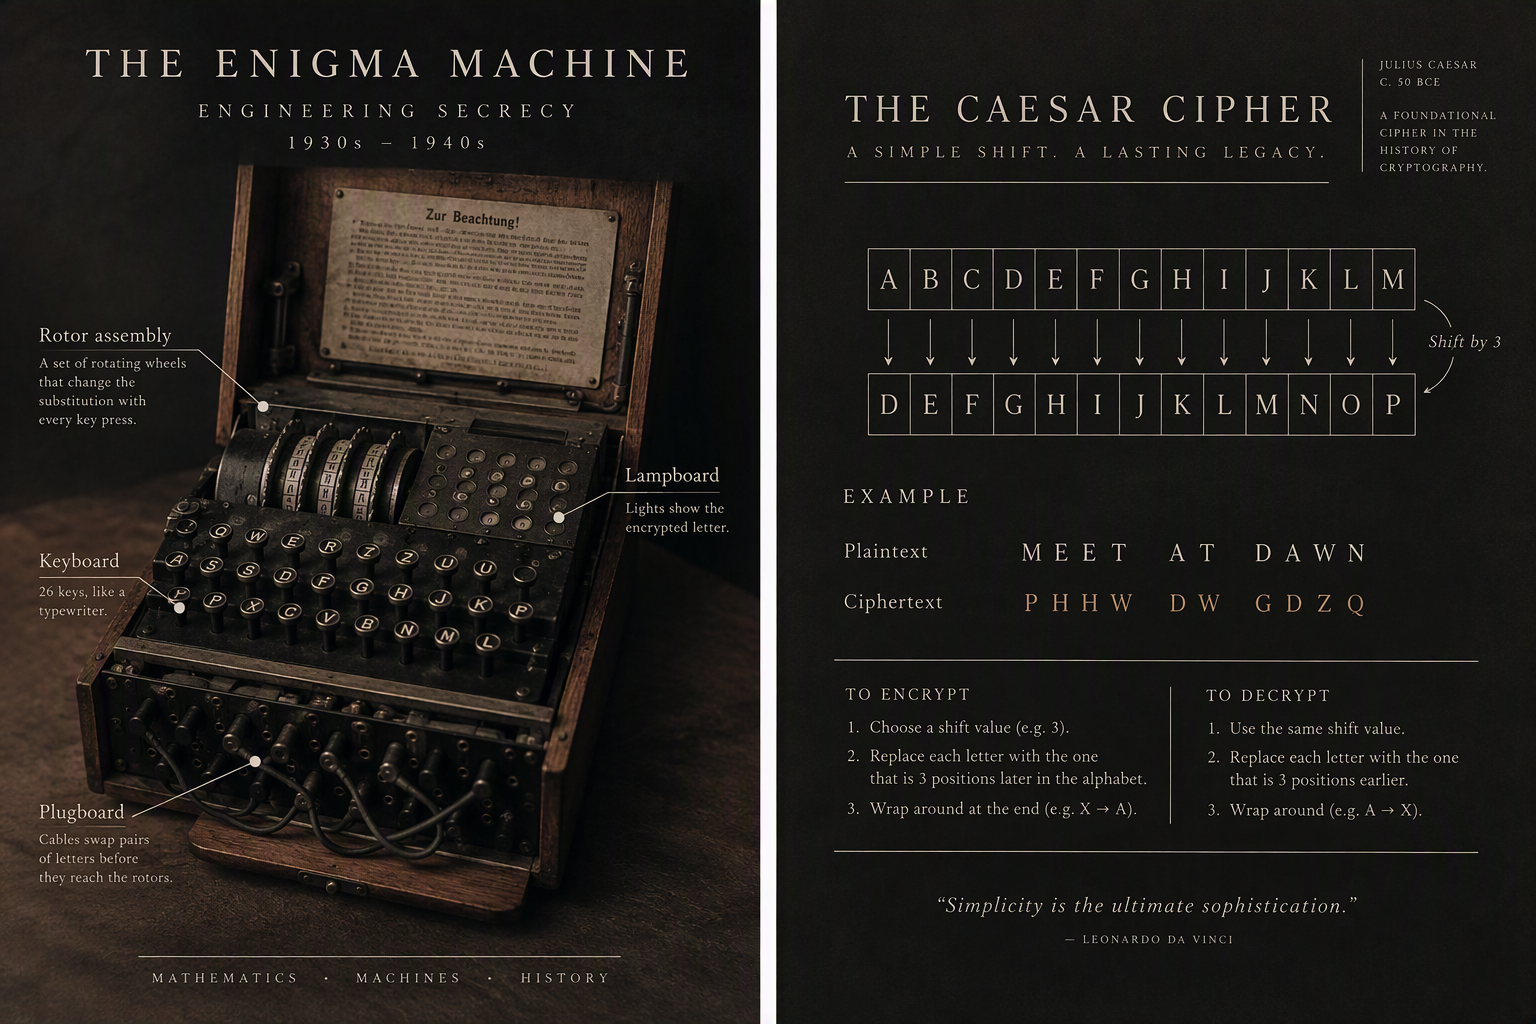
The Caesar Shift Cipher A famous Roman technique, this cipher involved shifting letters by a predetermined number, most commonly three, so that the recipient could shift them back to retrieve the original plaintext.
The Renaissance and Mechanical Eras The polyalphabetic cipher now called Vigenère was described by Giovan Battista Bellaso in 1553 and later became associated with Blaise de Vigenère. By the early 20th century, sophisticated mechanical devices like the Enigma rotor machine provided advanced encryption for military and government use.
Modern Shift Following World War II, cryptography and cryptanalysis increasingly drew on formal mathematics and computing, moving beyond character-based ciphers to algorithms that operate on binary data.
II. Fundamentals of Modern Cryptography
Modern cryptography is the cornerstone of computer security, built upon concepts from number theory, probability, and computational complexity. Unlike approaches that depend on hiding the method, modern systems generally use publicly known algorithms and rely on correctly managed keys and well-understood security assumptions.
The Basic Cryptosystem Model
A standard cryptosystem consists of five essential components:
Plaintext: The original data to be protected.
Encryption Algorithm: A mathematical process that transforms plaintext into ciphertext.
Ciphertext: The scrambled version of the data that flows over public channels.
Decryption Algorithm: The process that reverses encryption to output the original plaintext.
Keys: Values used to seed the algorithms; these must be kept secret even if the algorithm is public.
III. Primary Security Services
Cryptography provides four fundamental services to ensure the security of digital information:
Confidentiality: Ensures that information remains inaccessible to unauthorized parties.
Data Integrity: Allows for the detection of any unauthorized alterations to data during transmission or storage.
Authentication: Confirms the identity of the sender (message authentication) or the specific entity, such as a website (entity authentication).
Non-repudiation: Digital signatures can provide evidence that a key signed data, supporting accountability; they do not by themselves prove who controlled the key or prevent every denial of an action.
IV. Modern Cryptographic Methods
Cryptography is primarily divided into two categories based on how they handle keys:
1. Symmetric Key Encryption (Secret Key)
This method uses the same key for both encryption and decryption.
Advantages: Significantly faster and requires less processing power than asymmetric methods.
Example: AES is a widely standardized modern symmetric cipher. DES is obsolete, and 3DES has been withdrawn for new protection.
Challenges: Parties need a secure way to establish and manage the shared key. Key-agreement protocols can establish a key over an open network, but the parties still need to authenticate the exchange.
2. Asymmetric Key Encryption (Public Key)
Introduced in the 20th century, this method uses a mathematically related pair of keys: a public key and a private key.
Mechanics: In public-key encryption, data encrypted with a recipient's public key can be decrypted with the corresponding private key. Digital signatures use keys in a different way: the private key signs and the public key verifies.
Examples: RSA is one public-key algorithm. Internet protocols typically use public-key cryptography to authenticate or establish keys, then symmetric encryption for bulk data.
Challenges: Usually slower for bulk data and requires an authenticated way to associate public keys with identities, such as a Public Key Infrastructure (PKI).
3. Hashing
A cryptographic hash function maps data to a fixed-length digest. It is designed to be infeasible to reverse or find a different input with the same digest; it is not encryption and has no decryption key.
For password storage, do not use a fast general-purpose hash such as SHA-256 by itself. Store a unique salt and a password-hashing/KDF result, using a purpose-built, tunable function such as Argon2id or an appropriate PBKDF2 configuration. Verify a login by applying the same parameters and comparing the result safely.
V. Future Trends
Large-scale quantum computers could threaten some widely used public-key algorithms. Two different approaches are often confused:
Quantum Cryptography Quantum key distribution uses quantum states to establish keys and can reveal certain interception attempts under its protocol assumptions. It requires specialized infrastructure and is not a general replacement for encryption or a guarantee of secure endpoints.
Homomorphic Encryption Homomorphic encryption allows specified computations on ciphertexts, so a holder of the data may receive a result without seeing the plaintext. It can reduce exposure to a computing provider, but does not make a system “completely secure”; performance, implementation, access control, and the threat model still matter.